Practical insights on web development, app development, UI/UX design and digital marketing from the LeafyWings Technology team.

DPDP Act for Clinics: A Patient Data Checklist Before May 2027
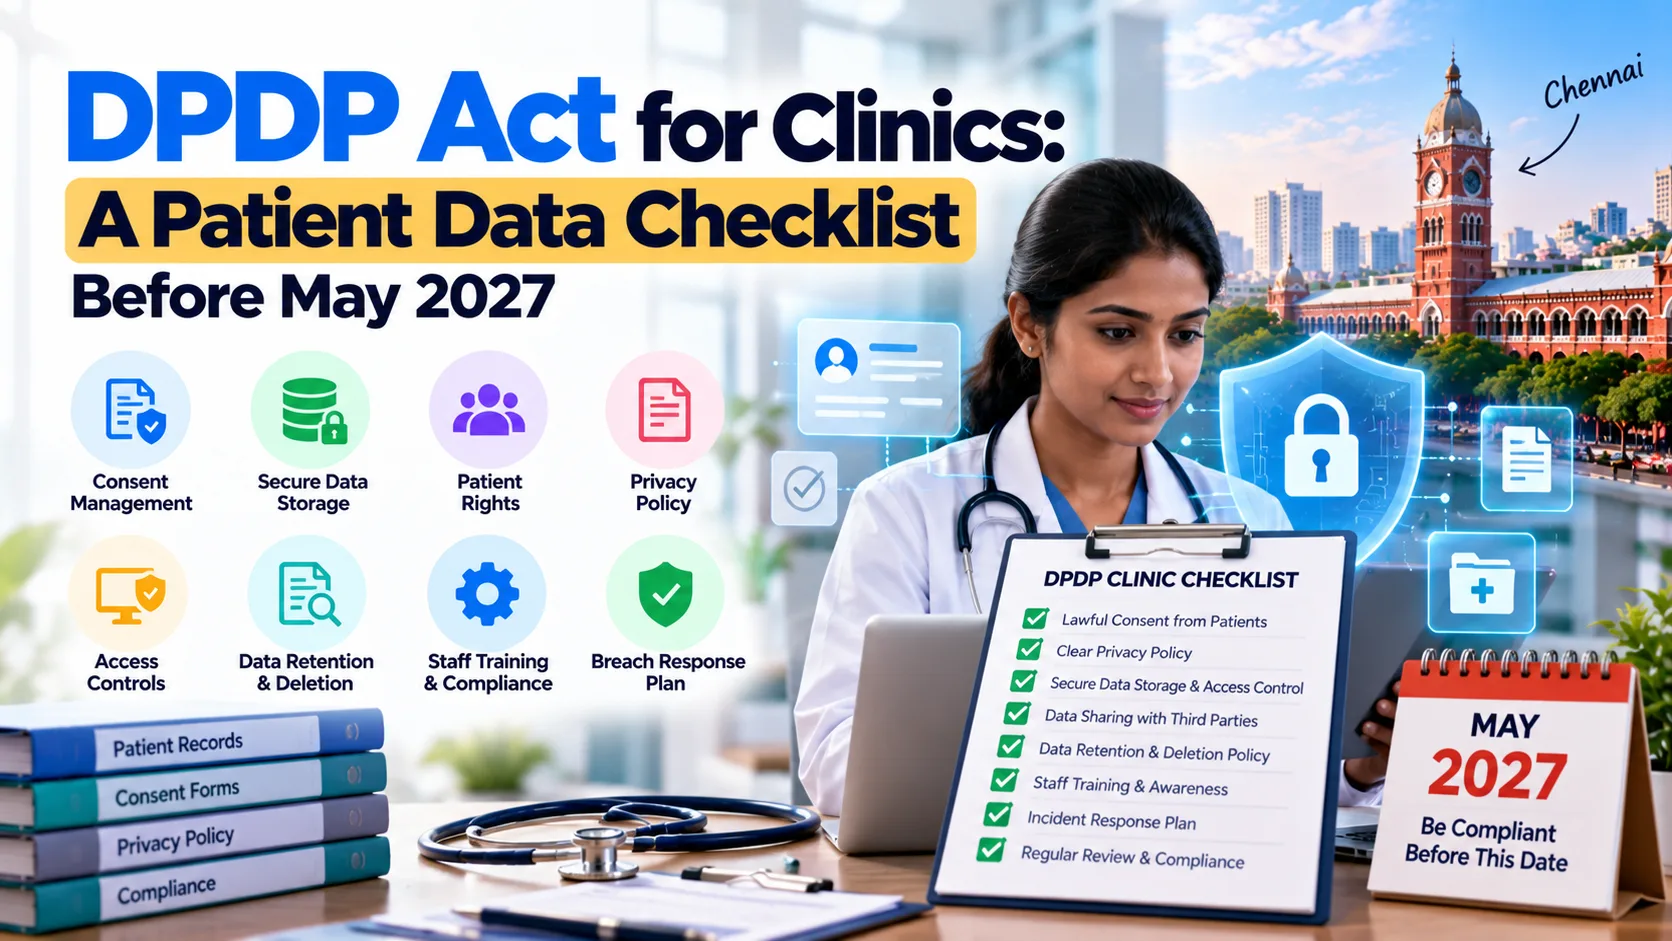
India's Digital Personal Data Protection (DPDP) Act, 2023, marks a pivotal shift in how personal data is handled. While the full implementation for many sectors is still some time away, clinics and healthcare providers face a crucial deadline: May 2027. This isn't just another regulatory hurdle; it's an opportunity to solidify patient trust and enhance your clinic's operational integrity. Understanding the specific implications of the DPDP Act for clinics is essential, as patient data is among the most sensitive information you handle. Are you ready? This guide provides a practical checklist to ensure your clinic is fully prepared.
Decoding the DPDP Act for Clinics: What You Need to Know
The DPDP Act establishes a framework for processing digital personal data in India. For clinics, this means a rigorous approach to collecting, storing, and using patient information. At its core, the Act emphasizes consent, purpose limitation, data minimization, and accountability. Every piece of information your clinic collects, from appointment schedules to medical histories and billing details, falls under this purview. The Act applies to all clinics, regardless of size, that process personal data digitally within India, or even outside if it's for offering goods or services to data principals in India. Ignoring these regulations could lead to significant penalties and reputational damage.
Why Early Preparation for DPDP Compliance is Non-Negotiable
While May 2027 might seem distant, the complexities of overhauling data management practices require substantial lead time. For clinics, patient data isn't just a record; it's the foundation of care. Non-compliance with the DPDP Act for clinics can result in hefty fines, loss of patient trust, and even legal action. Proactive preparation allows your clinic to integrate these changes smoothly, without disrupting patient care or administrative workflows. It also positions your clinic as a trustworthy and responsible healthcare provider, a significant competitive advantage in today's privacy-conscious world. Don't wait until the last minute; start building your compliance framework today.
Your Essential Patient Data Checklist for DPDP Readiness
Getting your clinic ready for the DPDP Act involves several key steps. This checklist outlines the critical areas you must address:
1. Revisit and Revamp Your Consent Mechanisms
- Clear, Affirmative Consent: Ensure all patient data collection is based on explicit, informed, and unambiguous consent. Patients must understand what data is being collected, why, and how it will be used.
- Granular Consent: Offer options for patients to consent to specific types of data processing (e.g., treatment, research, marketing communications) rather than a blanket agreement.
- Easy Withdrawal: Make it simple for patients to withdraw their consent at any time, with clear procedures for doing so.
- Record Keeping: Maintain a robust system to record and prove consent for every patient.
2. Inventory and Map All Patient Data
- Data Audit: Identify all personal data your clinic collects, processes, stores, and shares. This includes patient records, appointment data, billing information, and staff data.
- Data Flow Mapping: Understand where patient data originates, where it's stored, who has access, and how it moves through your systems and with third parties.
- Purpose Limitation: Ensure data is collected only for specific, legitimate purposes and not used for anything else without fresh consent.
- Data Minimization: Collect only the data that is absolutely necessary for the stated purpose. Regularly review and delete data that is no longer required.
3. Fortify Your Data Security Measures
- Access Controls: Implement strong access controls, ensuring only authorized personnel can access sensitive patient data based on their role.
- Encryption: Encrypt sensitive patient data, both at rest and in transit, to protect it from unauthorized access.
- Regular Backups: Establish robust data backup and recovery procedures to prevent data loss.
- Cybersecurity Protocols: Employ firewalls, antivirus software, and intrusion detection systems. Regularly update all software and systems.
4. Develop Robust Data Breach Protocols
- Incident Response Plan: Create a clear, actionable plan for identifying, assessing, and responding to data breaches.
- Notification Procedures: Define how and when to notify affected patients and the Data Protection Board of India in the event of a breach, as required by the Act.
- Post-Breach Review: Establish a process for reviewing breaches to improve security measures and prevent future incidents.
5. Train Your Clinic Staff
- Mandatory Training: Conduct regular training sessions for all staff members on DPDP Act requirements, data handling best practices, and security protocols.
- Awareness: Foster a culture of data privacy within your clinic, ensuring everyone understands their role in protecting patient information.
6. Review Third-Party Vendor Agreements
- Data Processor Agreements: Ensure all third-party vendors (e.g., EMR providers, billing software, cloud services) who process patient data on your behalf are also DPDP compliant.
- Contractual Obligations: Update contracts to include data protection clauses that align with the DPDP Act, clearly defining responsibilities and liabilities.
Beyond Compliance: Building Trust with the DPDP Act for Clinics
Complying with the DPDP Act for clinics is more than just avoiding penalties; it's about cementing your reputation as a responsible and ethical healthcare provider. Patients entrust you with their most personal information, and demonstrating a strong commitment to data privacy significantly enhances that trust. By proactively implementing these measures, your clinic not only meets legal obligations but also strengthens its foundation of patient confidence, fostering loyalty and positive word-of-mouth referrals.
Ready Your Clinic for the DPDP Act: Don't Wait Until 2027
The May 2027 deadline for the DPDP Act for clinics is rapidly approaching, and the time to act is now. Preparing your clinic for these comprehensive data protection rules requires a strategic approach and expert guidance. Don't let the complexities of compliance overwhelm you. Partner with LeafyWings Technology to navigate these changes seamlessly. Our team specializes in helping businesses like yours implement robust data privacy frameworks, ensuring your clinic is not just compliant but also thriving in a data-protected future. Contact us today to secure your clinic's data integrity and patient trust.
Related posts
Blog Categories
Recent Posts
-
Google Ads vs Facebook Ads for Chennai Businesses
November 03, 2026 -
Clinic Management Software in Chennai: What It Costs an...
November 02, 2026 -
How to Choose a UI/UX Design Company in Chennai: 10 Que...
October 30, 2026 -
DPDP Rules Website Checklist for Indian Small Businesse...
October 27, 2026 -
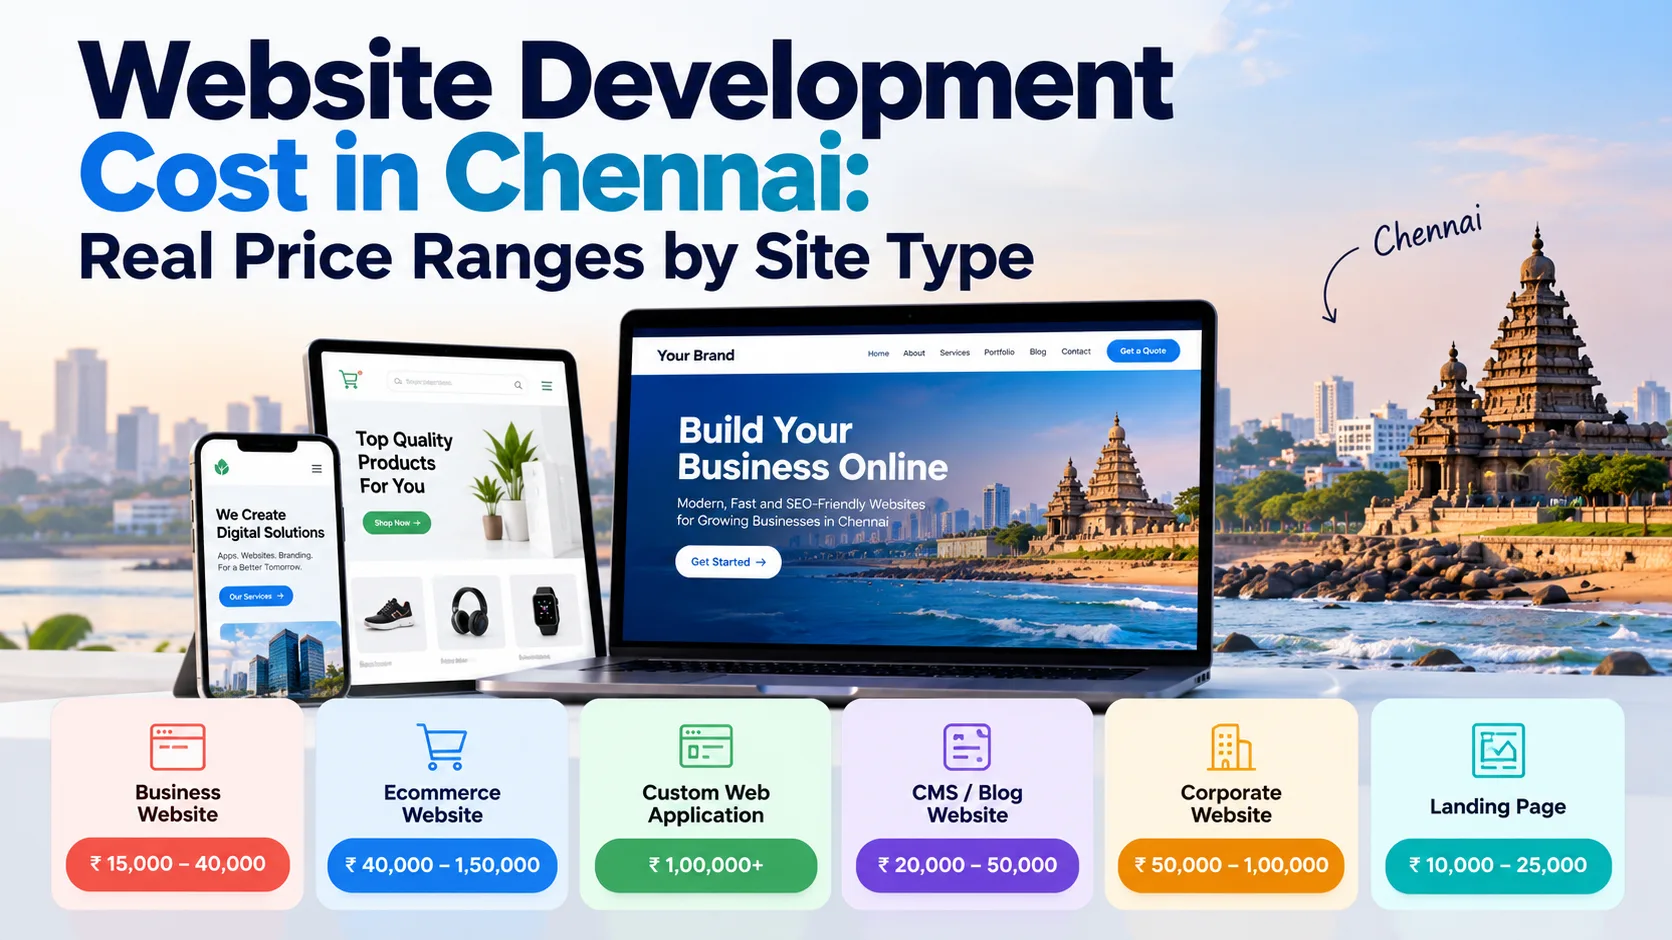
Website Development Cost in Chennai: Real Price Ranges...
October 20, 2026